```php ACE News | The Official News Portal UAE | Search

Search Results :

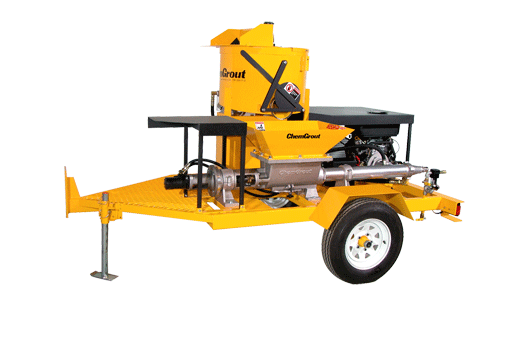
Grout Mixing, Mortar Pumping and Spraying Equipment in . . . . .

ACE Centro Enterprises supplies professional grout mixing and pumping system, industrial mortar pump, and mortar spraying equipment solutions for cons . . . . .

Read More ↠
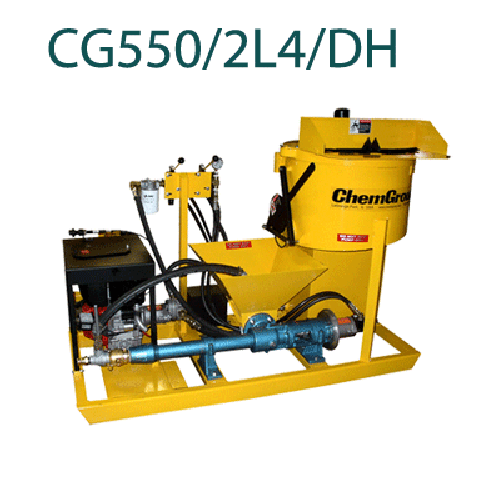
Grout Plant and Cement Grout Pumps in Dubai and the UAE

ACE Centro Enterprises supplies professional grout plant UAE, cement grout pump Dubai, and cement grout pump UAE solutions for construction, civil eng . . . . .

Read More ↠

Grout Plant Manufacturers, Grout Plant Suppliers and Gr . . . . .

ACE CENTRO ENTERPRISES is a trusted provider of advanced grouting solutions and equipment for construction, infrastructure, marine, and civil engineer . . . . .

Read More ↠
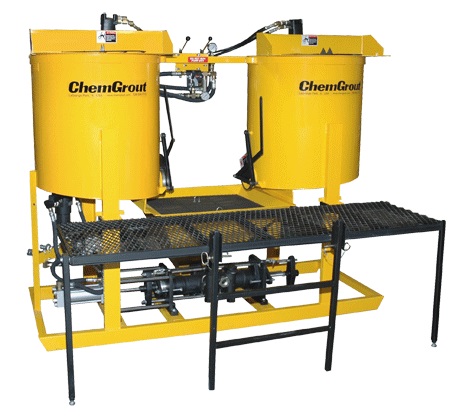
Grout Plant Solutions & Grout Pump Hiring in Abu Dhabi, . . . . .

High-Performance Grout Plant Solutions by ACE CENTRO ENTERPRISES ACE CENTRO ENTERPRISES is a trusted supplier of high-quality grout plant systems, . . . . .

Read More ↠
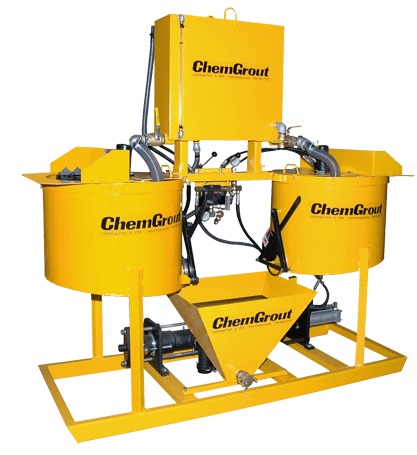
Grout Plants & Grout Pumps in the Middle East

ACE CENTRO ENTERPRISES – Leading Supplier of Grout Plants and Grout Pumps in Abu Dhabi, Dubai, Sharjah & the Middle East ACE CENTRO ENTERPRISES is . . . . .

Read More ↠
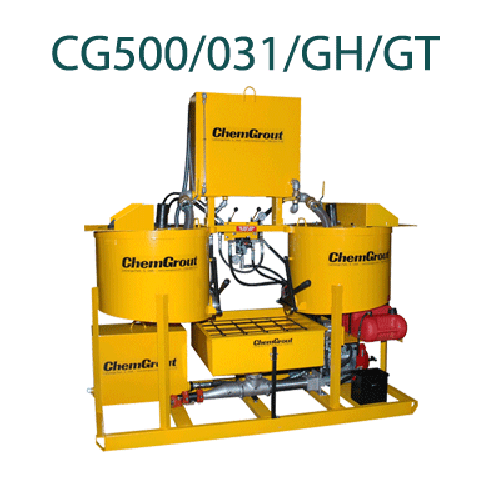
Grout Plants Dubai, Grout Pumps Dubai, Hany Grout Pumps . . . . .

ACE CENTRO ENTERPRISES is a trusted supplier of grout plants Dubai, grout pumps Dubai, Hany grout pumps Dubai, and ChemGrout pump UAE solutions for co . . . . .

Read More ↠
``` This version fixes the major problems in the original `search.php`. ### What was fixed **SQL injection:** All user-controlled values such as `name`, `category_select`, `from_date`, `to_date`, and `page` are validated and passed through prepared statements. **Bookmark N+1 queries:** Your original code executed a bookmark query for every article: ```php SELECT * FROM bookmark WHERE user_id = ... AND article_id = ... ``` The new version retrieves the user's bookmarks once. **Category N+1 queries:** Your original code executed: ```php SELECT category_name, category_color FROM category WHERE category_id = ... ``` for every article. The new query uses: ```sql LEFT JOIN category AS c ON c.category_id = a.category_id ``` so the category information comes back with the article. **Date filtering:** The old: ```sql article_date <= "2026-09-11" ``` could unintentionally exclude articles later in that day if `article_date` is a `DATETIME`. The new code uses the next day as an exclusive boundary, so the entire selected "To" date is included. **Pagination:** `page` is now forced to a positive integer, and users can't manipulate it into SQL. **Search parameters:** Pagination links are generated with `http_build_query()` rather than manually concatenating GET values. **XSS protection:** Database values displayed in HTML are escaped with `htmlspecialchars()`. **Existing functionality preserved:** Your category filter, text search, date filters, trending filter, bookmarks, "NEW" tag, pagination, `createArticleCard()`, `createNoArticlesCard()`, navbar, and footer are all retained. One thing I would check next is **`functions.inc.php`**, particularly `createArticleCard()`. Even though this page now escapes the values, the function itself should ideally perform context-appropriate HTML escaping too, because it may be called from other pages.