```php ACE News | The Official News Portal UAE | Search

Search Results :

Underwater Pipeline Barge Solutions in UAE & Middle Eas . . . . .

ACE CENTRO ENTERPRISES provides specialized and high-performance underwater pipeline barge solutions across Abu Dhabi, Dubai, Sharjah, and the Middle . . . . .

Read More ↠

Underwater Pipeline Installation Barge Precision Offsh . . . . .

ACE CENTRO ENTERPRISES provides specialized Underwater Pipeline Installation Barge solutions in UAE designed for safe, precise, and efficient offsho . . . . .

Read More ↠

Underwater Slurry Pumping System DRH400 Self-Propelled . . . . .

Efficient underwater slurry pumping system solutions are essential for deep-sea dredging, sediment transport, and heavy-duty marine operations. The DR . . . . .

Read More ↠
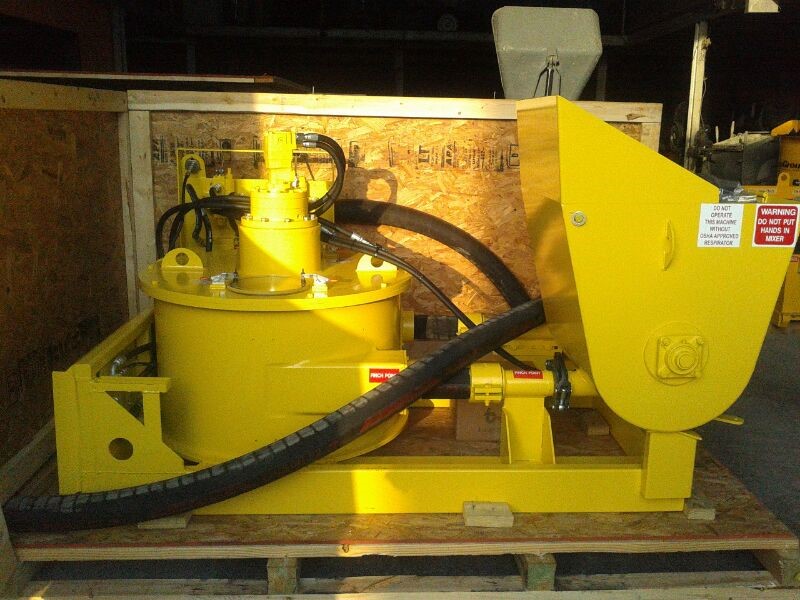
Universal Skid Steer Mount Pump: Discover the Blastcret . . . . .

Universal Skid Steer Mount Pump: Discover the Blastcrete RD6536 Looking for a reliable universal skid steer mount pump for concrete, grout, and sho . . . . .

Read More ↠
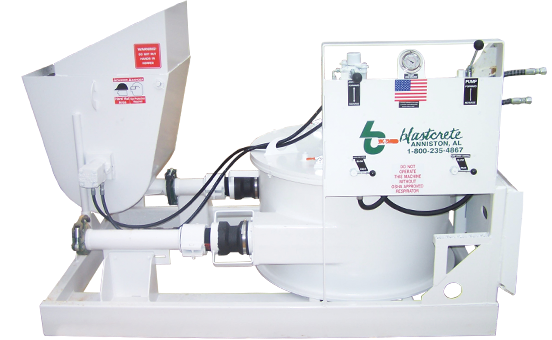
Universal Skid Steer Mount Pump: High-Performance RD653 . . . . .

Introduction to Universal Skid Steer Mount Pump A Universal Skid Steer Mount Pump is an essential piece of equipment in modern construction, design . . . . .

Read More ↠

Unloading Sump Pump UW Dredging Variable Speed Dredge . . . . .

Dragflow is a world leader in solid pumping solutions, with over 25 years of experience in manufacturing heavy-duty submersible dredging pumps and com . . . . .

Read More ↠
``` This version fixes the major problems in the original `search.php`. ### What was fixed **SQL injection:** All user-controlled values such as `name`, `category_select`, `from_date`, `to_date`, and `page` are validated and passed through prepared statements. **Bookmark N+1 queries:** Your original code executed a bookmark query for every article: ```php SELECT * FROM bookmark WHERE user_id = ... AND article_id = ... ``` The new version retrieves the user's bookmarks once. **Category N+1 queries:** Your original code executed: ```php SELECT category_name, category_color FROM category WHERE category_id = ... ``` for every article. The new query uses: ```sql LEFT JOIN category AS c ON c.category_id = a.category_id ``` so the category information comes back with the article. **Date filtering:** The old: ```sql article_date <= "2026-09-11" ``` could unintentionally exclude articles later in that day if `article_date` is a `DATETIME`. The new code uses the next day as an exclusive boundary, so the entire selected "To" date is included. **Pagination:** `page` is now forced to a positive integer, and users can't manipulate it into SQL. **Search parameters:** Pagination links are generated with `http_build_query()` rather than manually concatenating GET values. **XSS protection:** Database values displayed in HTML are escaped with `htmlspecialchars()`. **Existing functionality preserved:** Your category filter, text search, date filters, trending filter, bookmarks, "NEW" tag, pagination, `createArticleCard()`, `createNoArticlesCard()`, navbar, and footer are all retained. One thing I would check next is **`functions.inc.php`**, particularly `createArticleCard()`. Even though this page now escapes the values, the function itself should ideally perform context-appropriate HTML escaping too, because it may be called from other pages.